PHP2Shell, two vulnerabilities that have taken many services offline as they prepare updates to their systems. We don't cover exploits really here on Out of Games, but with this one being as large as it is you might be wondering why your favourite website or game isn't able to be accessed today.
We're going to try to not get too technical while we answer that question.
What's Going On?
Two PHP vulnerabilities were reported today, CVE-2026-109618 and CVE-2026-109619, which allow for a "Remote Code Execution". This is one of the more scary kinds of exploits to have available out in the wild because it allows an attacker to run any commands or code on a machine. This issue hits PHP versions 5.4 through 8.5 and the company has released patches today in the supported 8.2 through 8.5 interpreter releases and have also backported fixes to other no longer supported versions of the, though those programs have to be compiled yourself as they are unsupported.
In computer software, like a website, someone being able to visit and execute any kind of code is one of the most severe issues you can encounter. RCEs mean attackers can read, modify, and steal anything on a target system. So if you use a website that is exploited by an RCE, it's possible for those attackers to fetch the contents of the database, config files, secrets, source code, and more. They could also install backdoors onto systems so even after the hole is patched, they could retain access to a critical system, coming back later to do more damage.
One of the big problems with a PHP RCE is that it is one of the more common programming languages running on the web, and one that runs some of the largest websites which makes it a massive attack vector. Wikipedia for example runs on MediaWiki which uses PHP as its backend language. So with so many sites running PHP, you're talking about a massive amount of systems that have been vulnerable and with it becoming public knowledge are likely to be exploited.
PHP is sorta famous for people running very out of date software due to how common it is for smaller businesses and hobbyists to be running things like WordPress, which also relies on PHP, and they aren't exactly known for updating their software consistently. Even many shared webhosts will stay on older versions of PHP which is a critical oversight and allows their customers to be at risk for attacks.
I will say that in 2026 webhosts do seem to do a better job at keeping these up to date, though still, not enough care is taken when it comes to software security.
Cloudflare Beefs up Security
Cloudflare reported signs of early exploitation prior to the public patch release, and deployed temporary web application firewall rules as an attempted stopgap mitigation against the vulnerability for their customers, which is one of the benefits of having a large amount of the web behind them - us too - though that is not a proper replacement for updating your software!
Quote From Cloudflare Cloudflare has been part of a coordinated effort to deploy mitigations to protect the Internet, working with PHP foundation, OpenAI and Wiz among others. Cloudflare has developed and deployed web application firewall (WAF) protections since early October 2026, which were deployed about 9 hours ahead of public disclosure. Starting on October 21 3:02 am UTC, Cloudflare customers using our free or paid WAF were protected by default against php2shell.
Cloudflare successfully deployed multiple mitigations for all its customers while the vulnerability was leaked before the official release date and we observed attack traffic targeting our customers. We observed how attackers were mutating the attack payload to try to bypass our protections by tracking the volume of matches and cross-referencing with the rule logic.
Protecting against php2shell required more than standard request-based rules. Request data alone does not always provide enough evidence to distinguish an exploit from legitimate traffic. The origin’s response adds context, helping identify whether an exploit succeeded while reducing the risk of false positives.
To deliver this protection, we developed full transaction detection, a new Cloudflare WAF capability that combines signals from the request and response within the same HTTP transaction. Response rules can then block a matching origin response before it reaches the requester. The php2shell protections are the first managed detections we have released using this capability.
Websites Offline in Gaming
Many websites were taken offline in gaming, including:
Pokemon Company temporarily took down many of their sites and services.
Nintendo also took down many services as they addressed the vulnerability.
Yugipedia
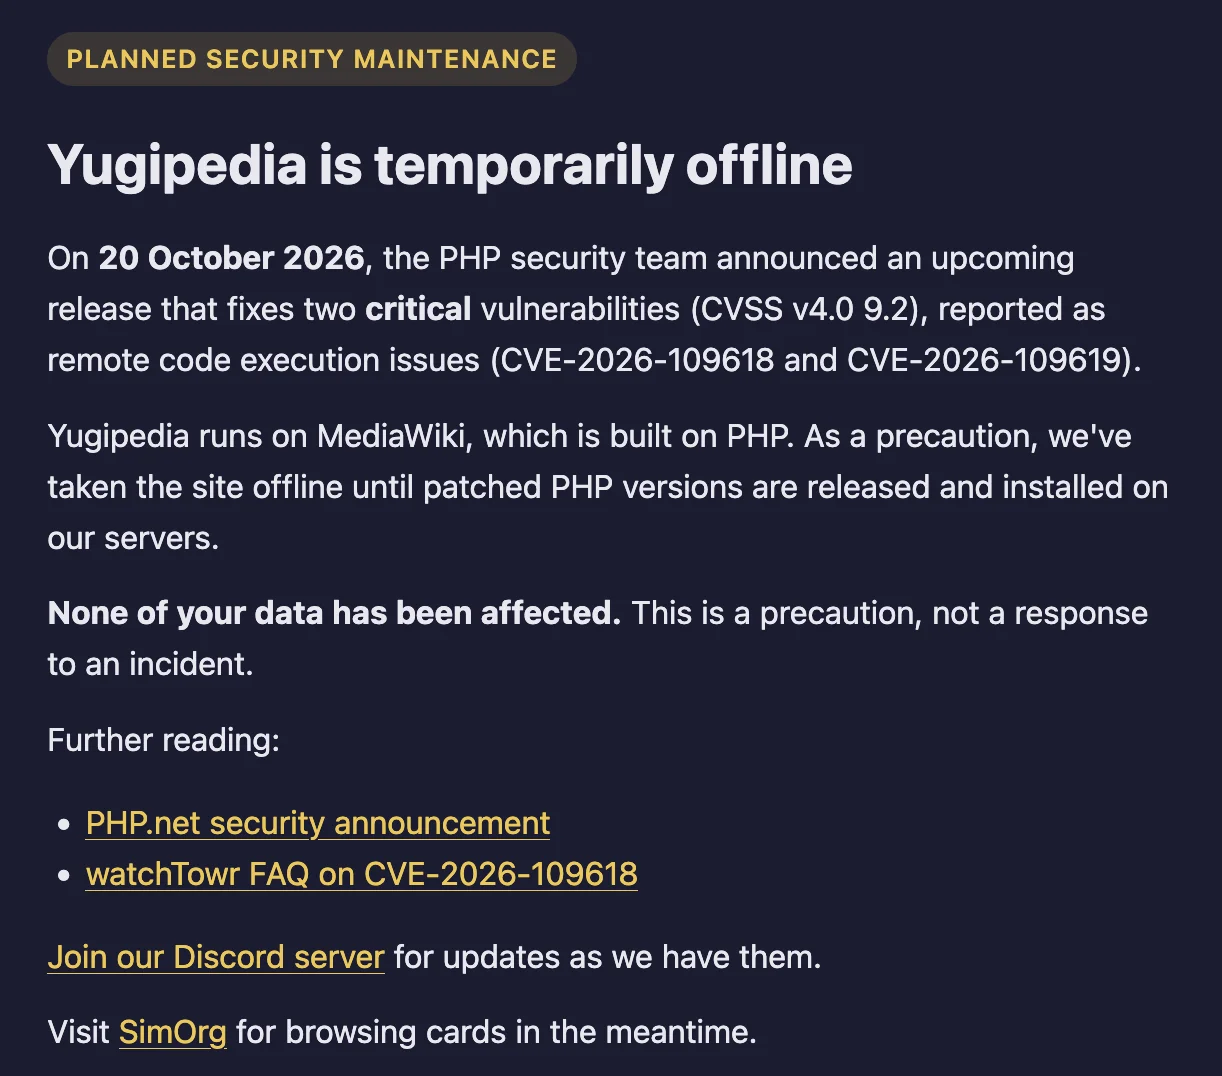
We could sit here and list out a ton of different sites, just know that some of the most popular content management systems run on PHP (Wikis, Forums, and WordPress) so this hits a ton of websites.
Is Out of Games Impacted?
No. We don't run any PHP on our systems; Our founder (me!) has thankfully not touched PHP in over a decade. Nothing on our website has been hit by the vulnerability and all our systems remain operational and as up to date as they can be.
How has your day been impacted due to outages?
Leave a Comment